
Pull request security review
Enclave checks pull request changes against the surrounding code and posts verified concerns as inline comments for engineers to review.
Get a demo
The workflow
How it works
Security teams cannot manually inspect every pull request. New endpoints, dependencies, and authorization changes can reach production before anyone has checked their impact.
Inspect the change
Agents examine the pull request alongside the surrounding code and relevant dependencies.
Check the concern
Potential issues go through verification before they become review feedback.
Respond in the PR
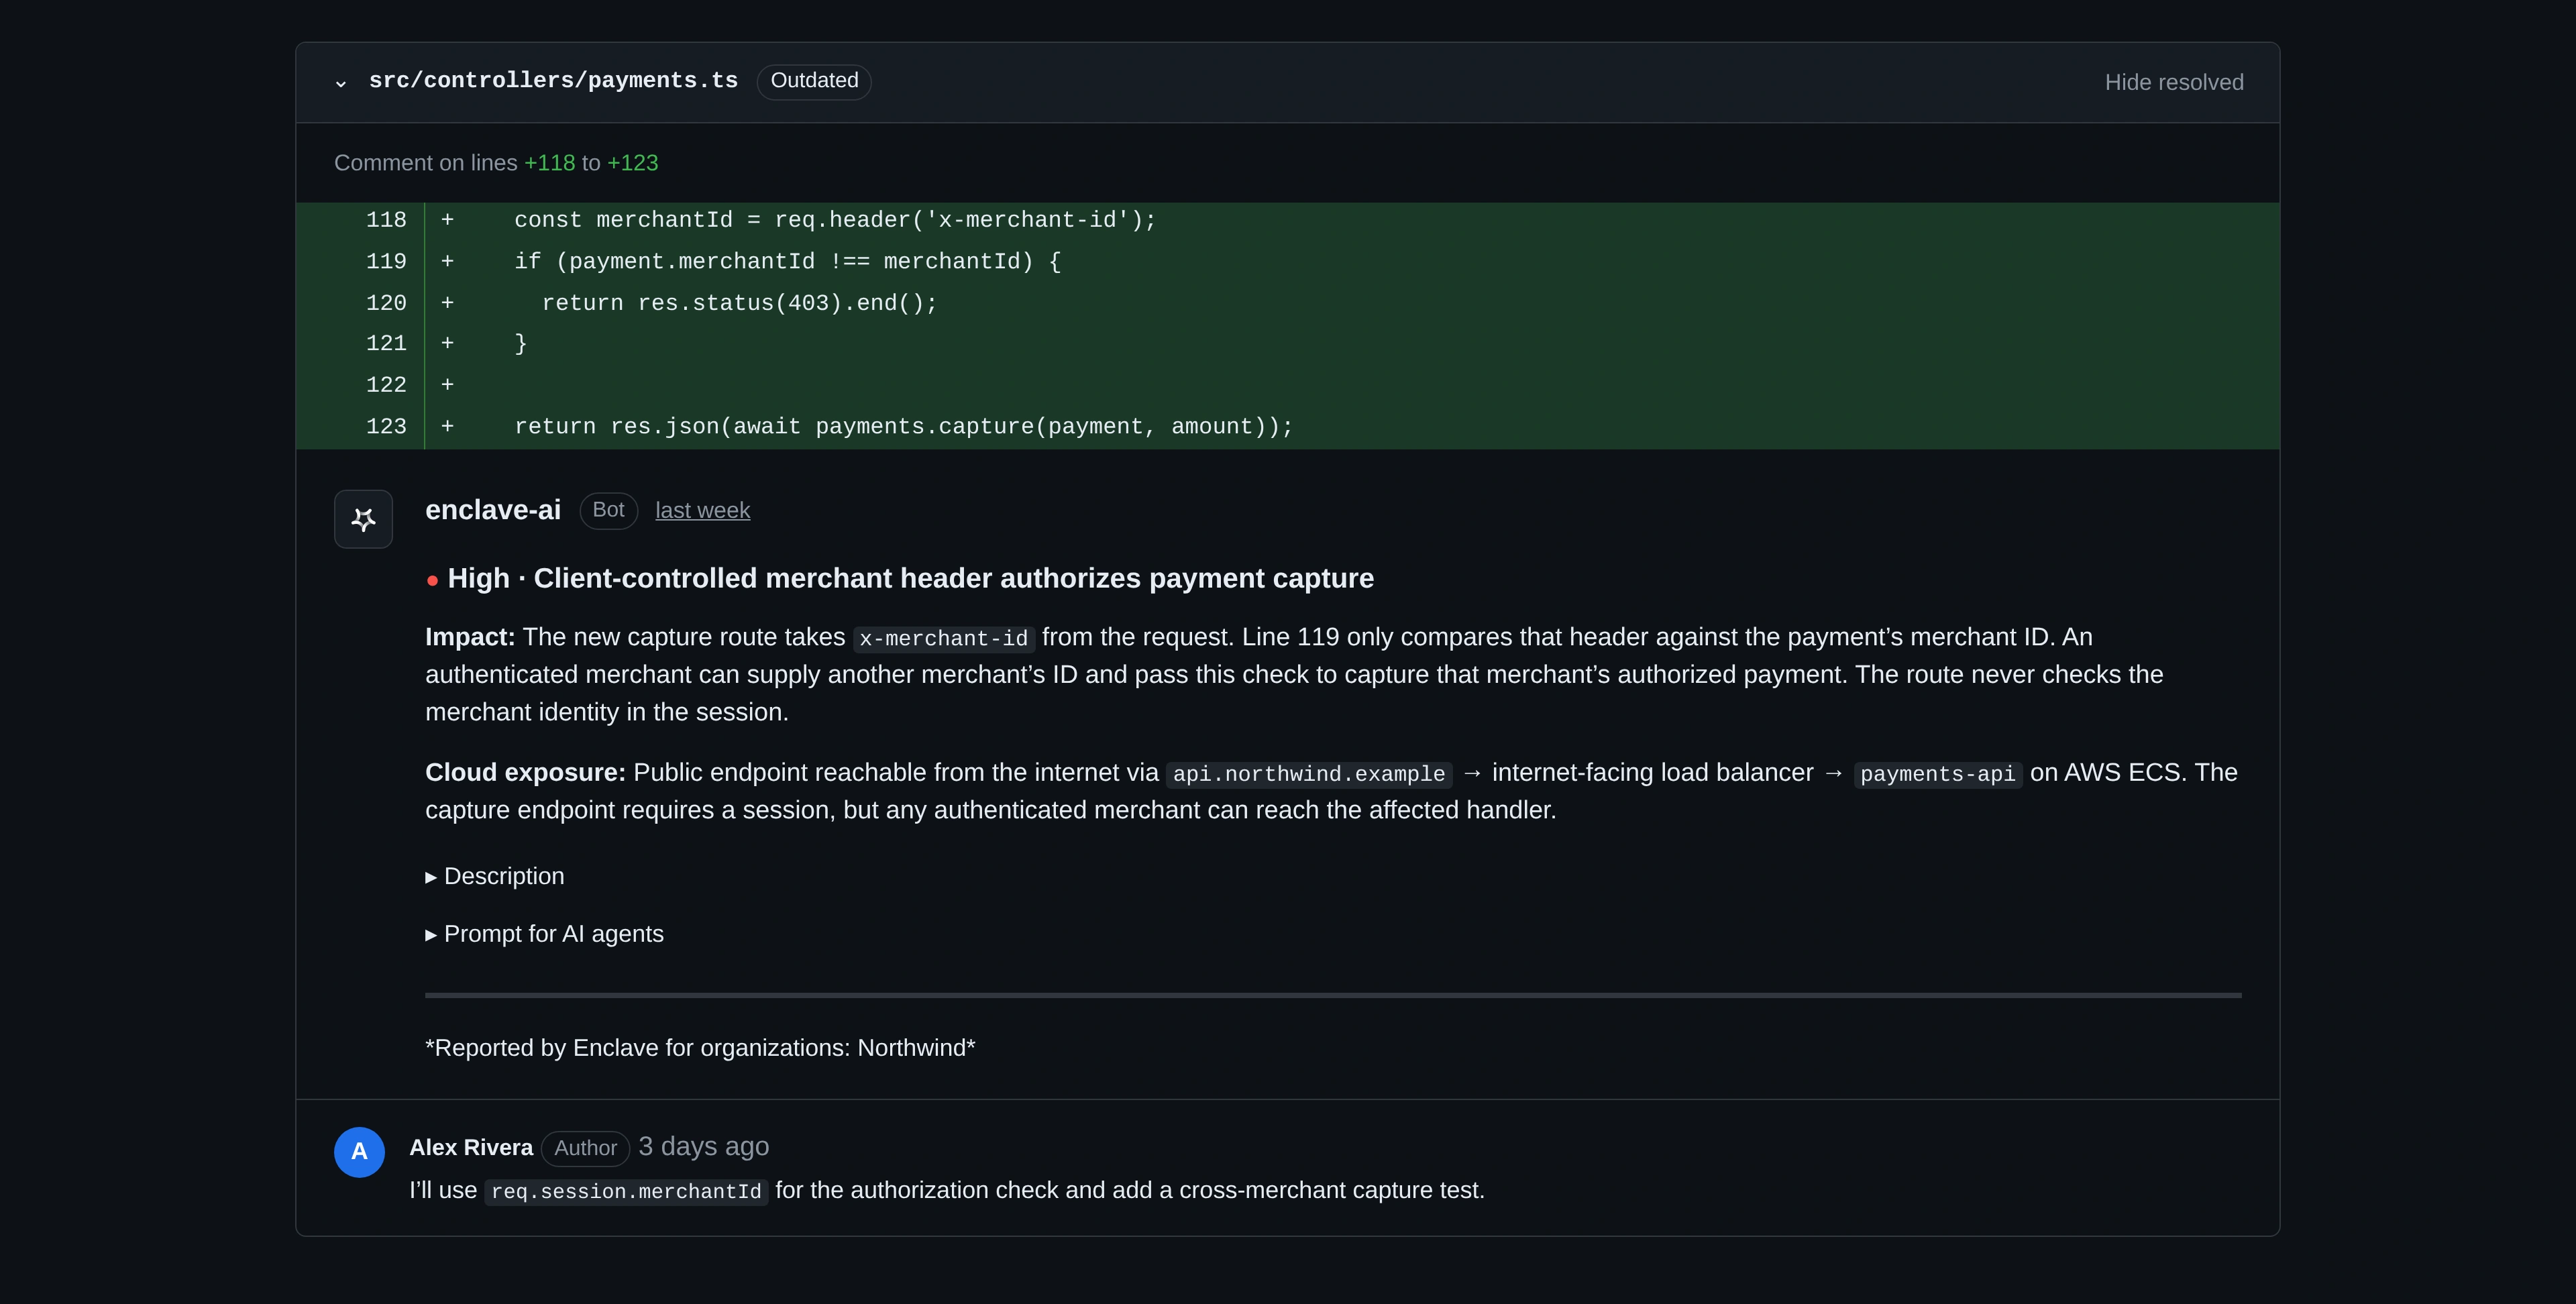
The result lands in the pull request as a comment and check for your team to review.
The result
An inline comment ties the concern to changed lines, its impact, supporting evidence, and a suggested fix.