
CVE monitoring
A new advisory should start an investigation, not a manual search across your stack. Enclave watches for new CVEs and checks whether the affected technology is present and exposed in your environment.
Get a demo
The workflow
How it works
A headline CVE does not tell you if your application uses the vulnerable path or whether it is reachable in your environment.
Watch new advisories
Agents track published CVEs and match them against what is known about your stack.
Check your exposure
They investigate affected dependencies, code paths, and cloud or infrastructure context.
Send confirmed exposure to triage
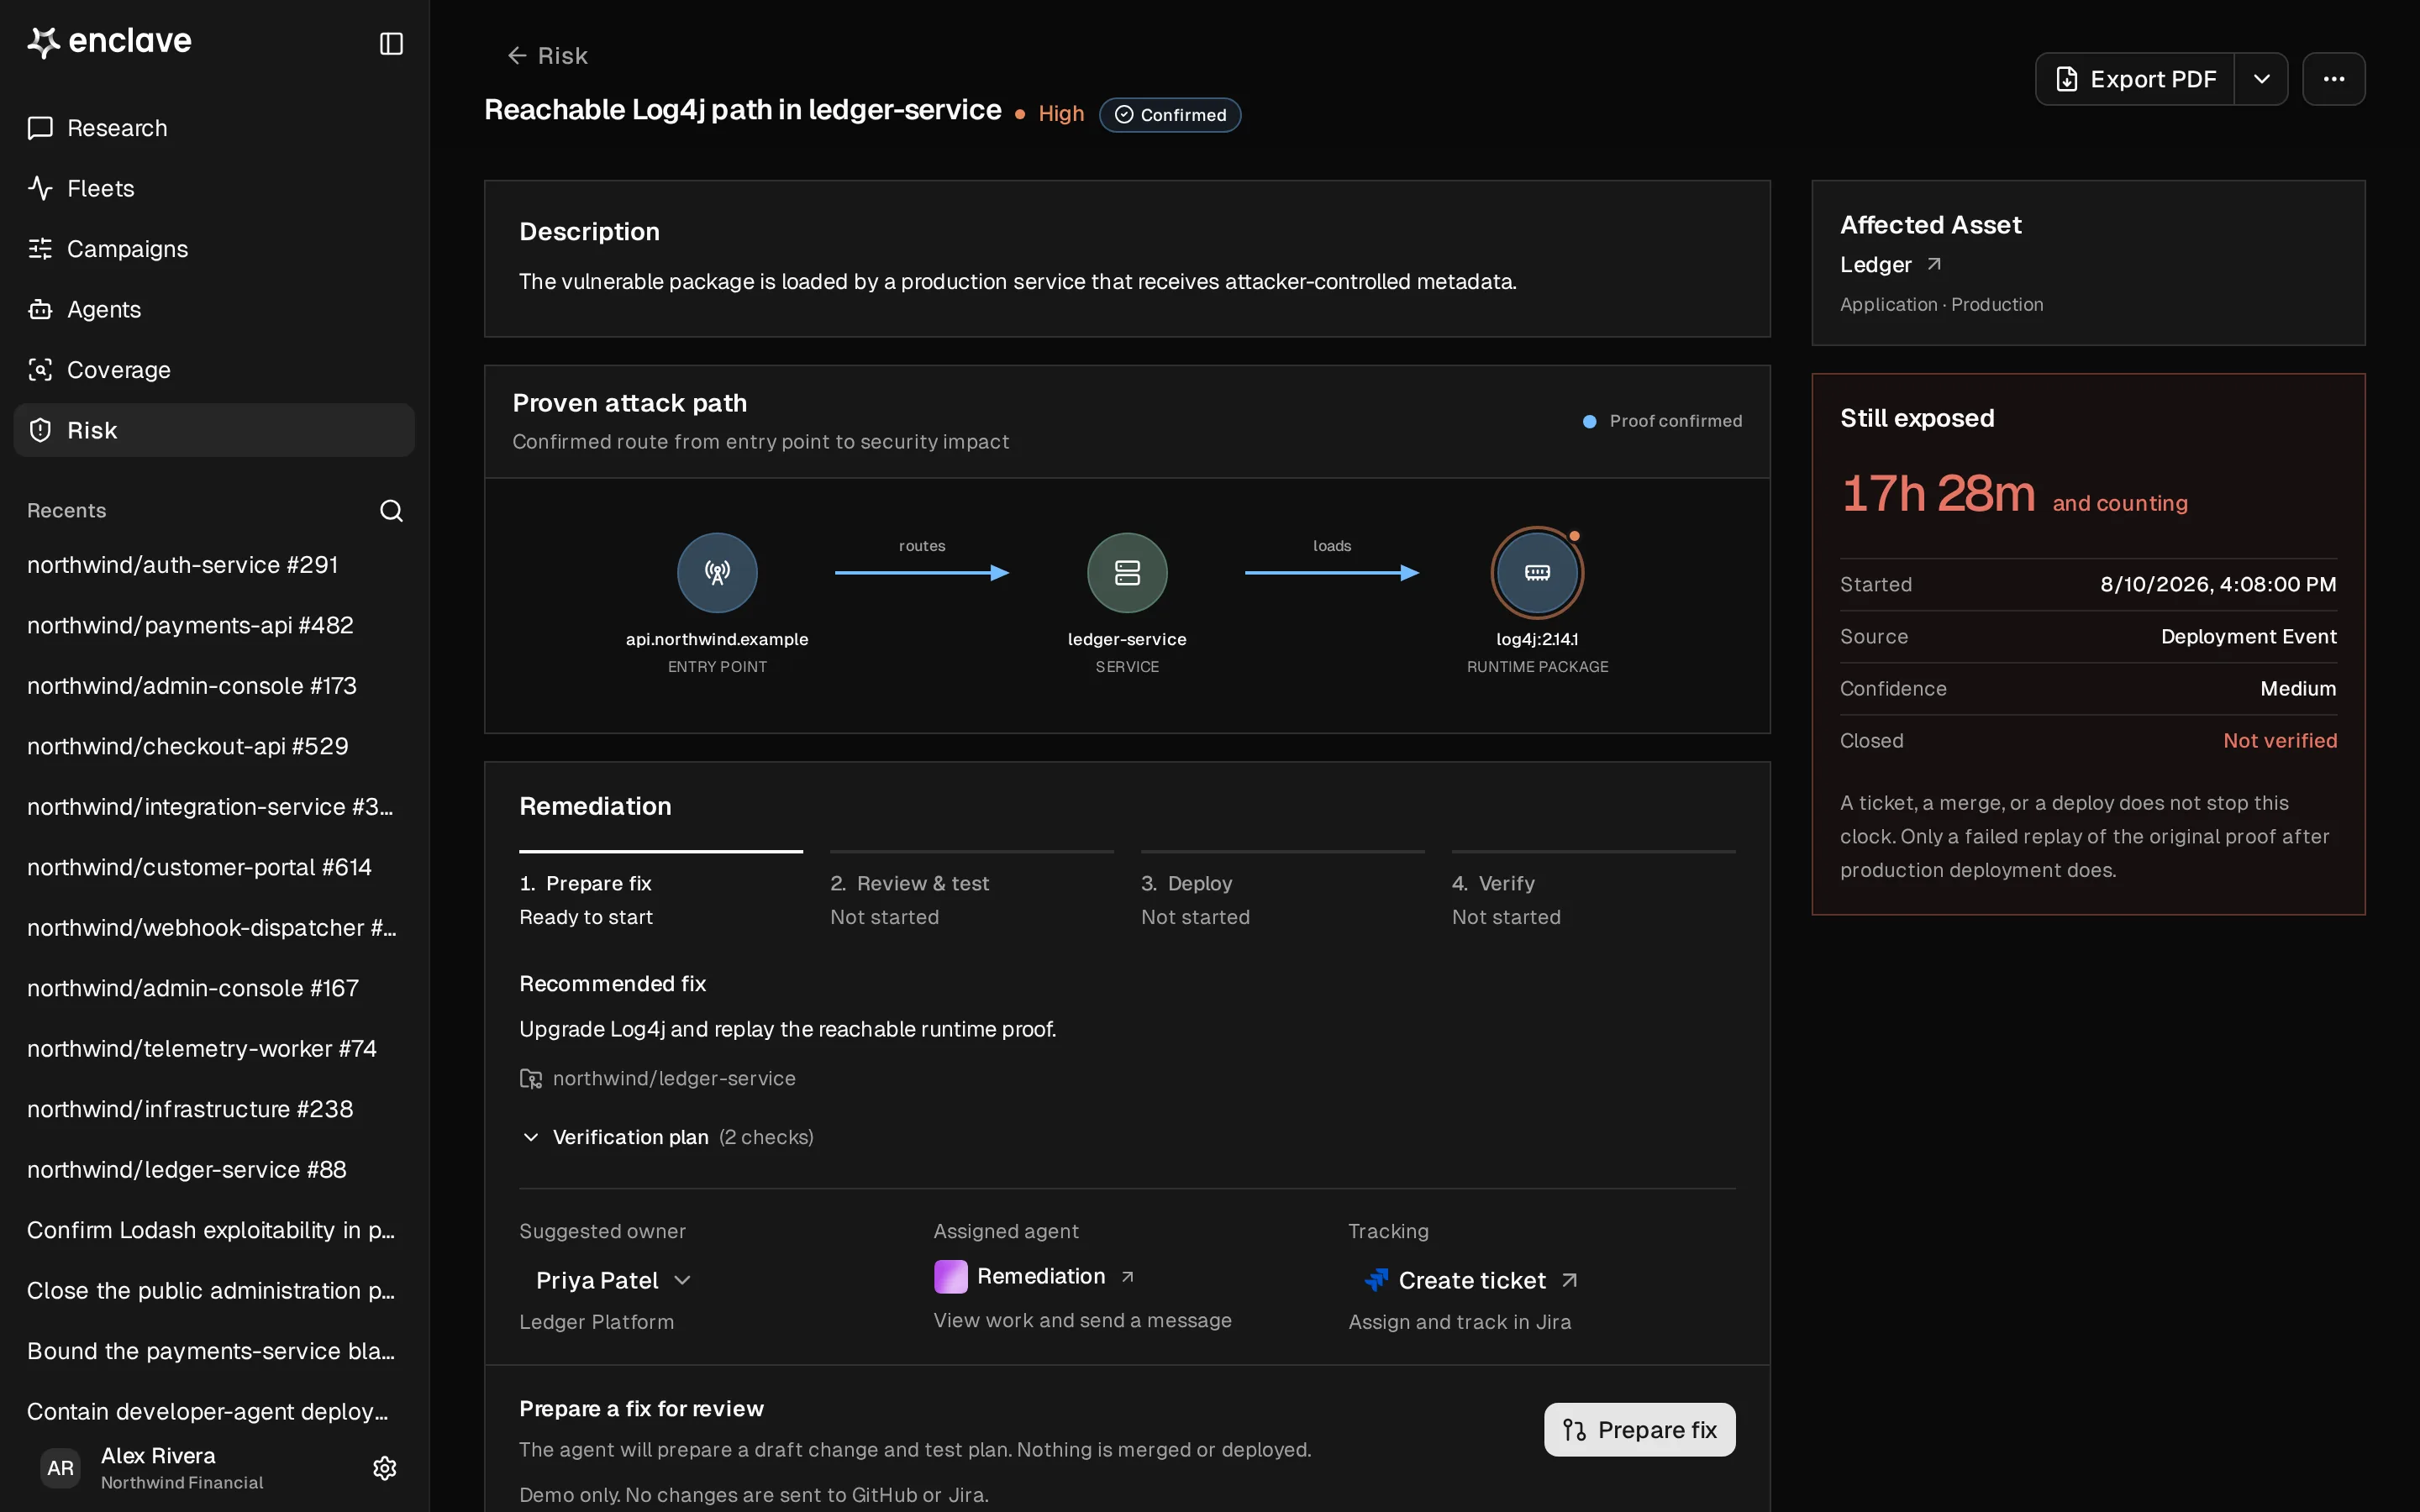
Confirmed exposure carries the affected asset and attack-path evidence into triage and remediation.
The result
An exposure record connects the advisory to the affected package, reachable entry point, and verification status.