
Code security review
Agents read the code behind your applications, trace how data and permissions move, and investigate weaknesses that a pattern match alone cannot explain.
Get a demo
The workflow
How it works
A file-level alert rarely tells you whether a weakness is reachable, how it relates to the rest of the system, or what an attacker could do with it.
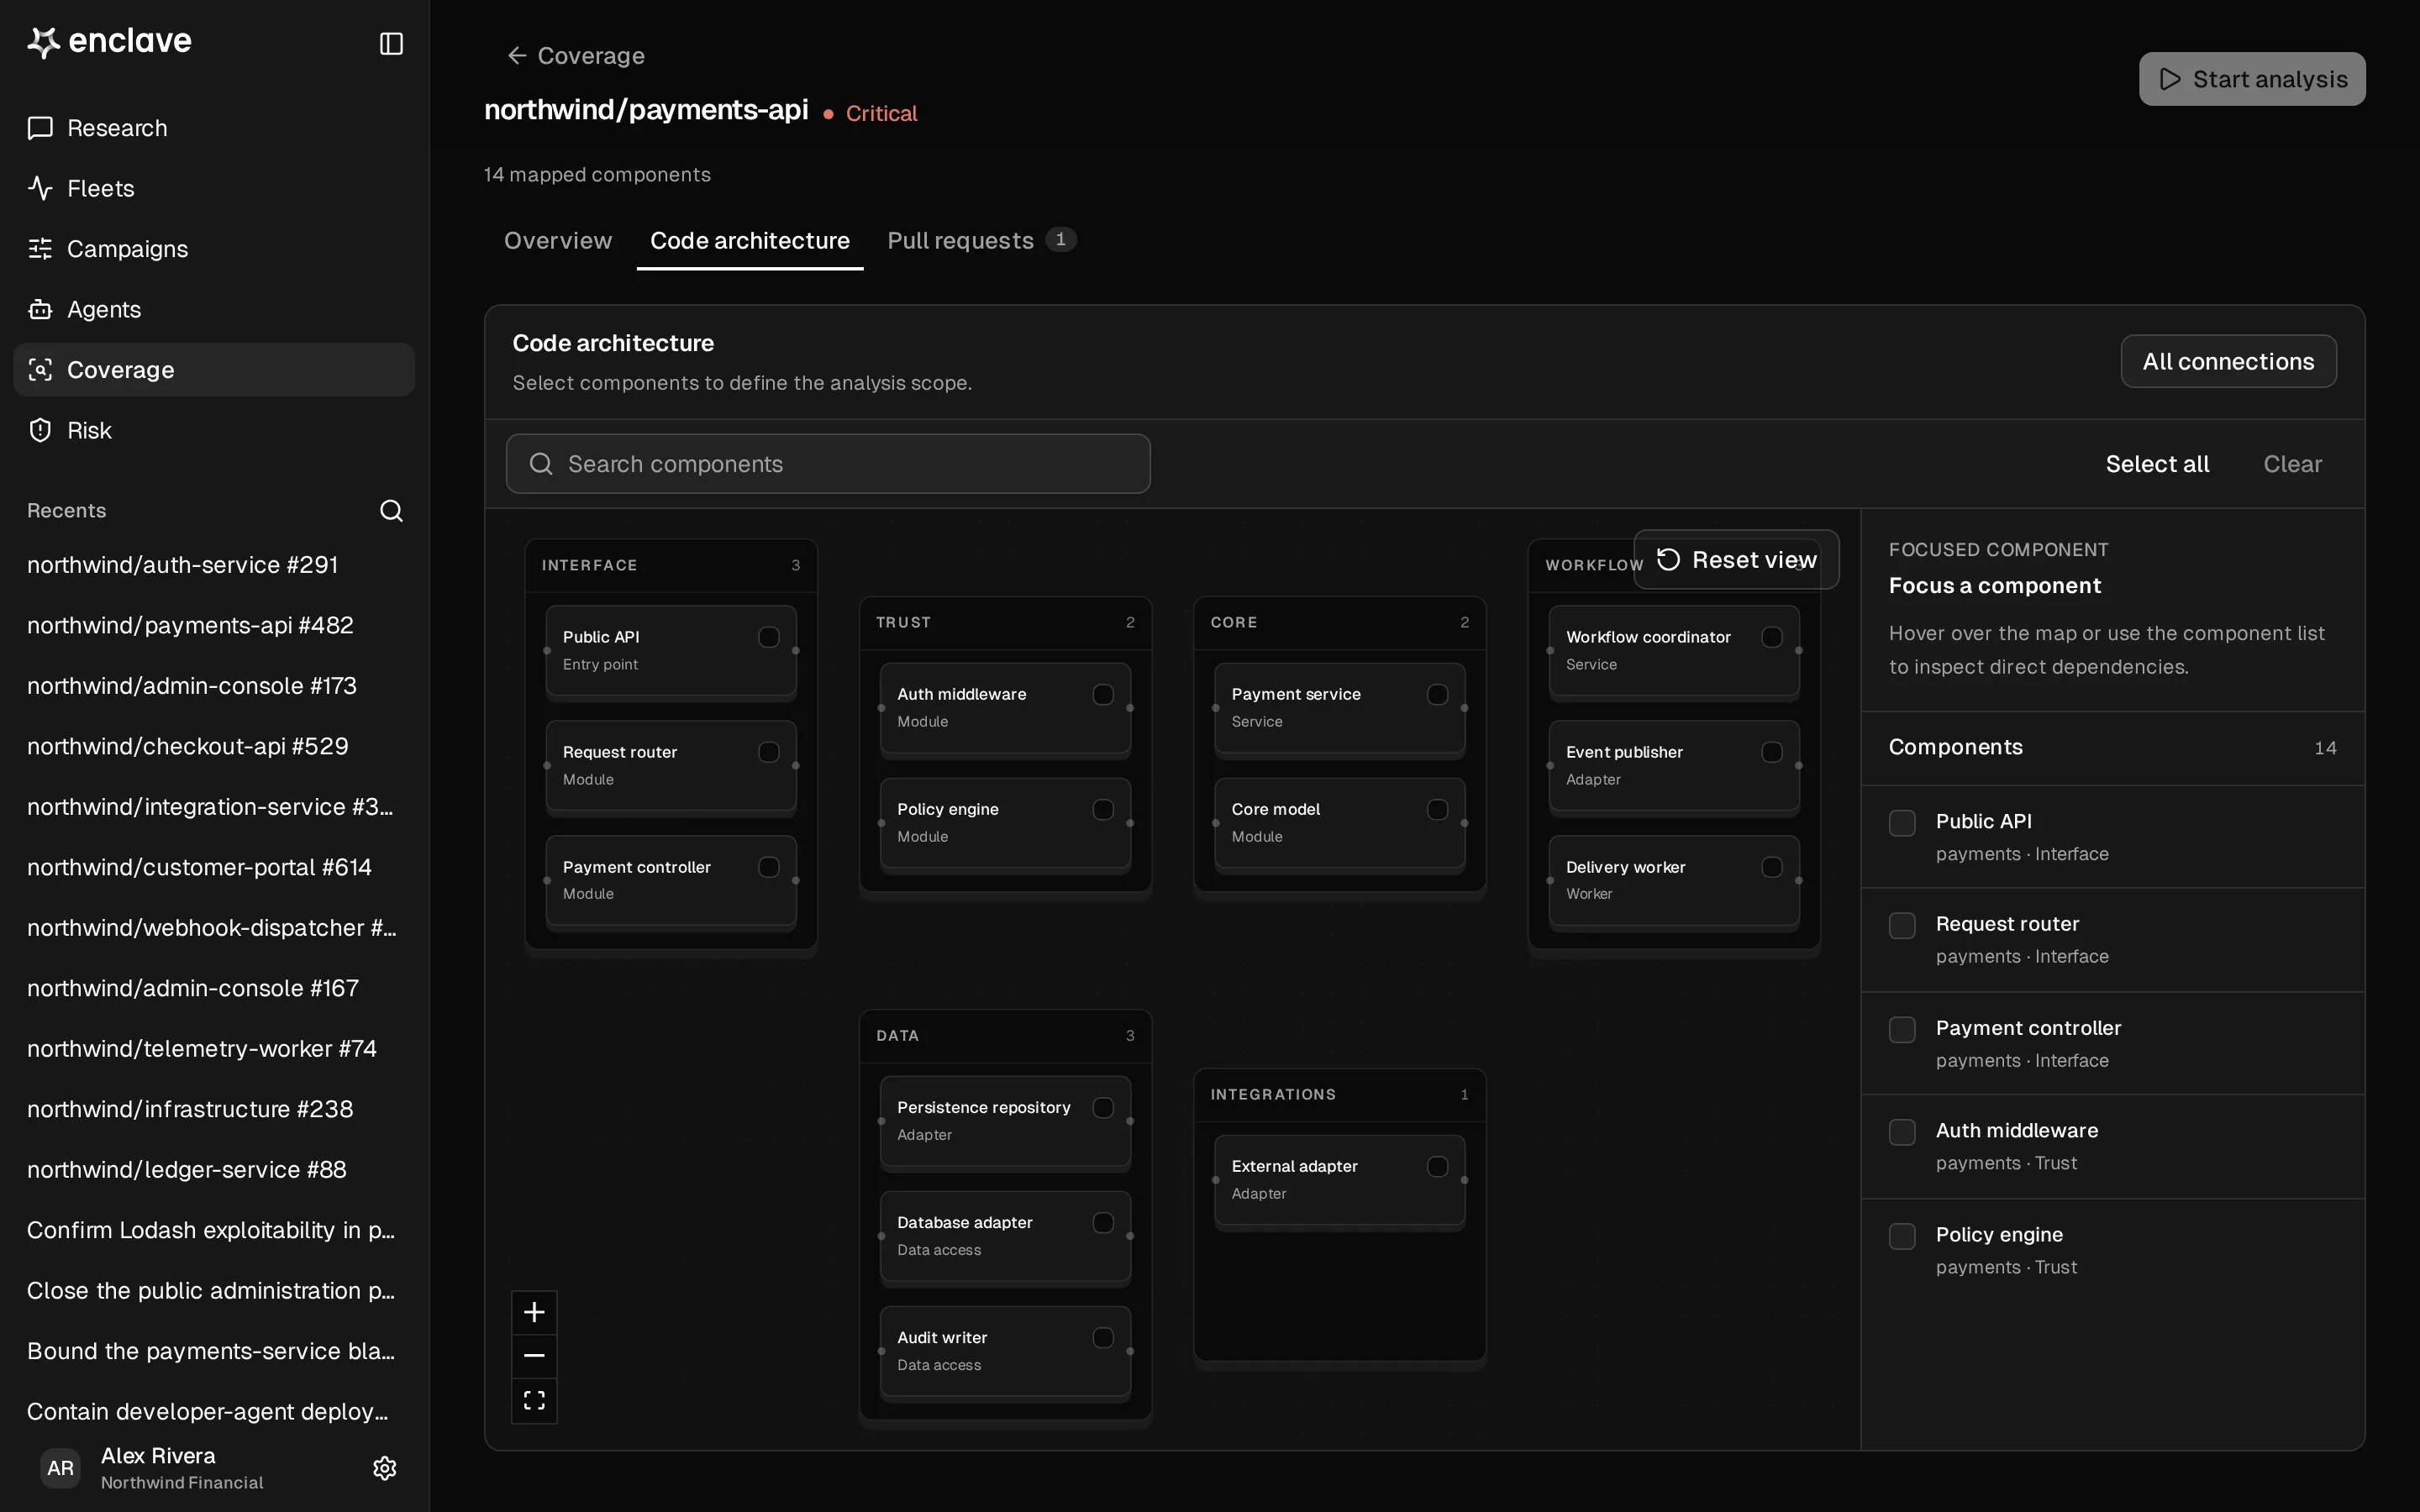
Understand the application
Agents map code components and their relationships before looking for risky paths.
Trace the weakness
They follow inputs, authorization decisions, and data flows across components.
Investigate the impact
Agents check whether the traced path can be reached and what data or permissions it exposes.
The result
Review findings with the affected code, reachable path, and evidence needed for triage.