
Dependency protection
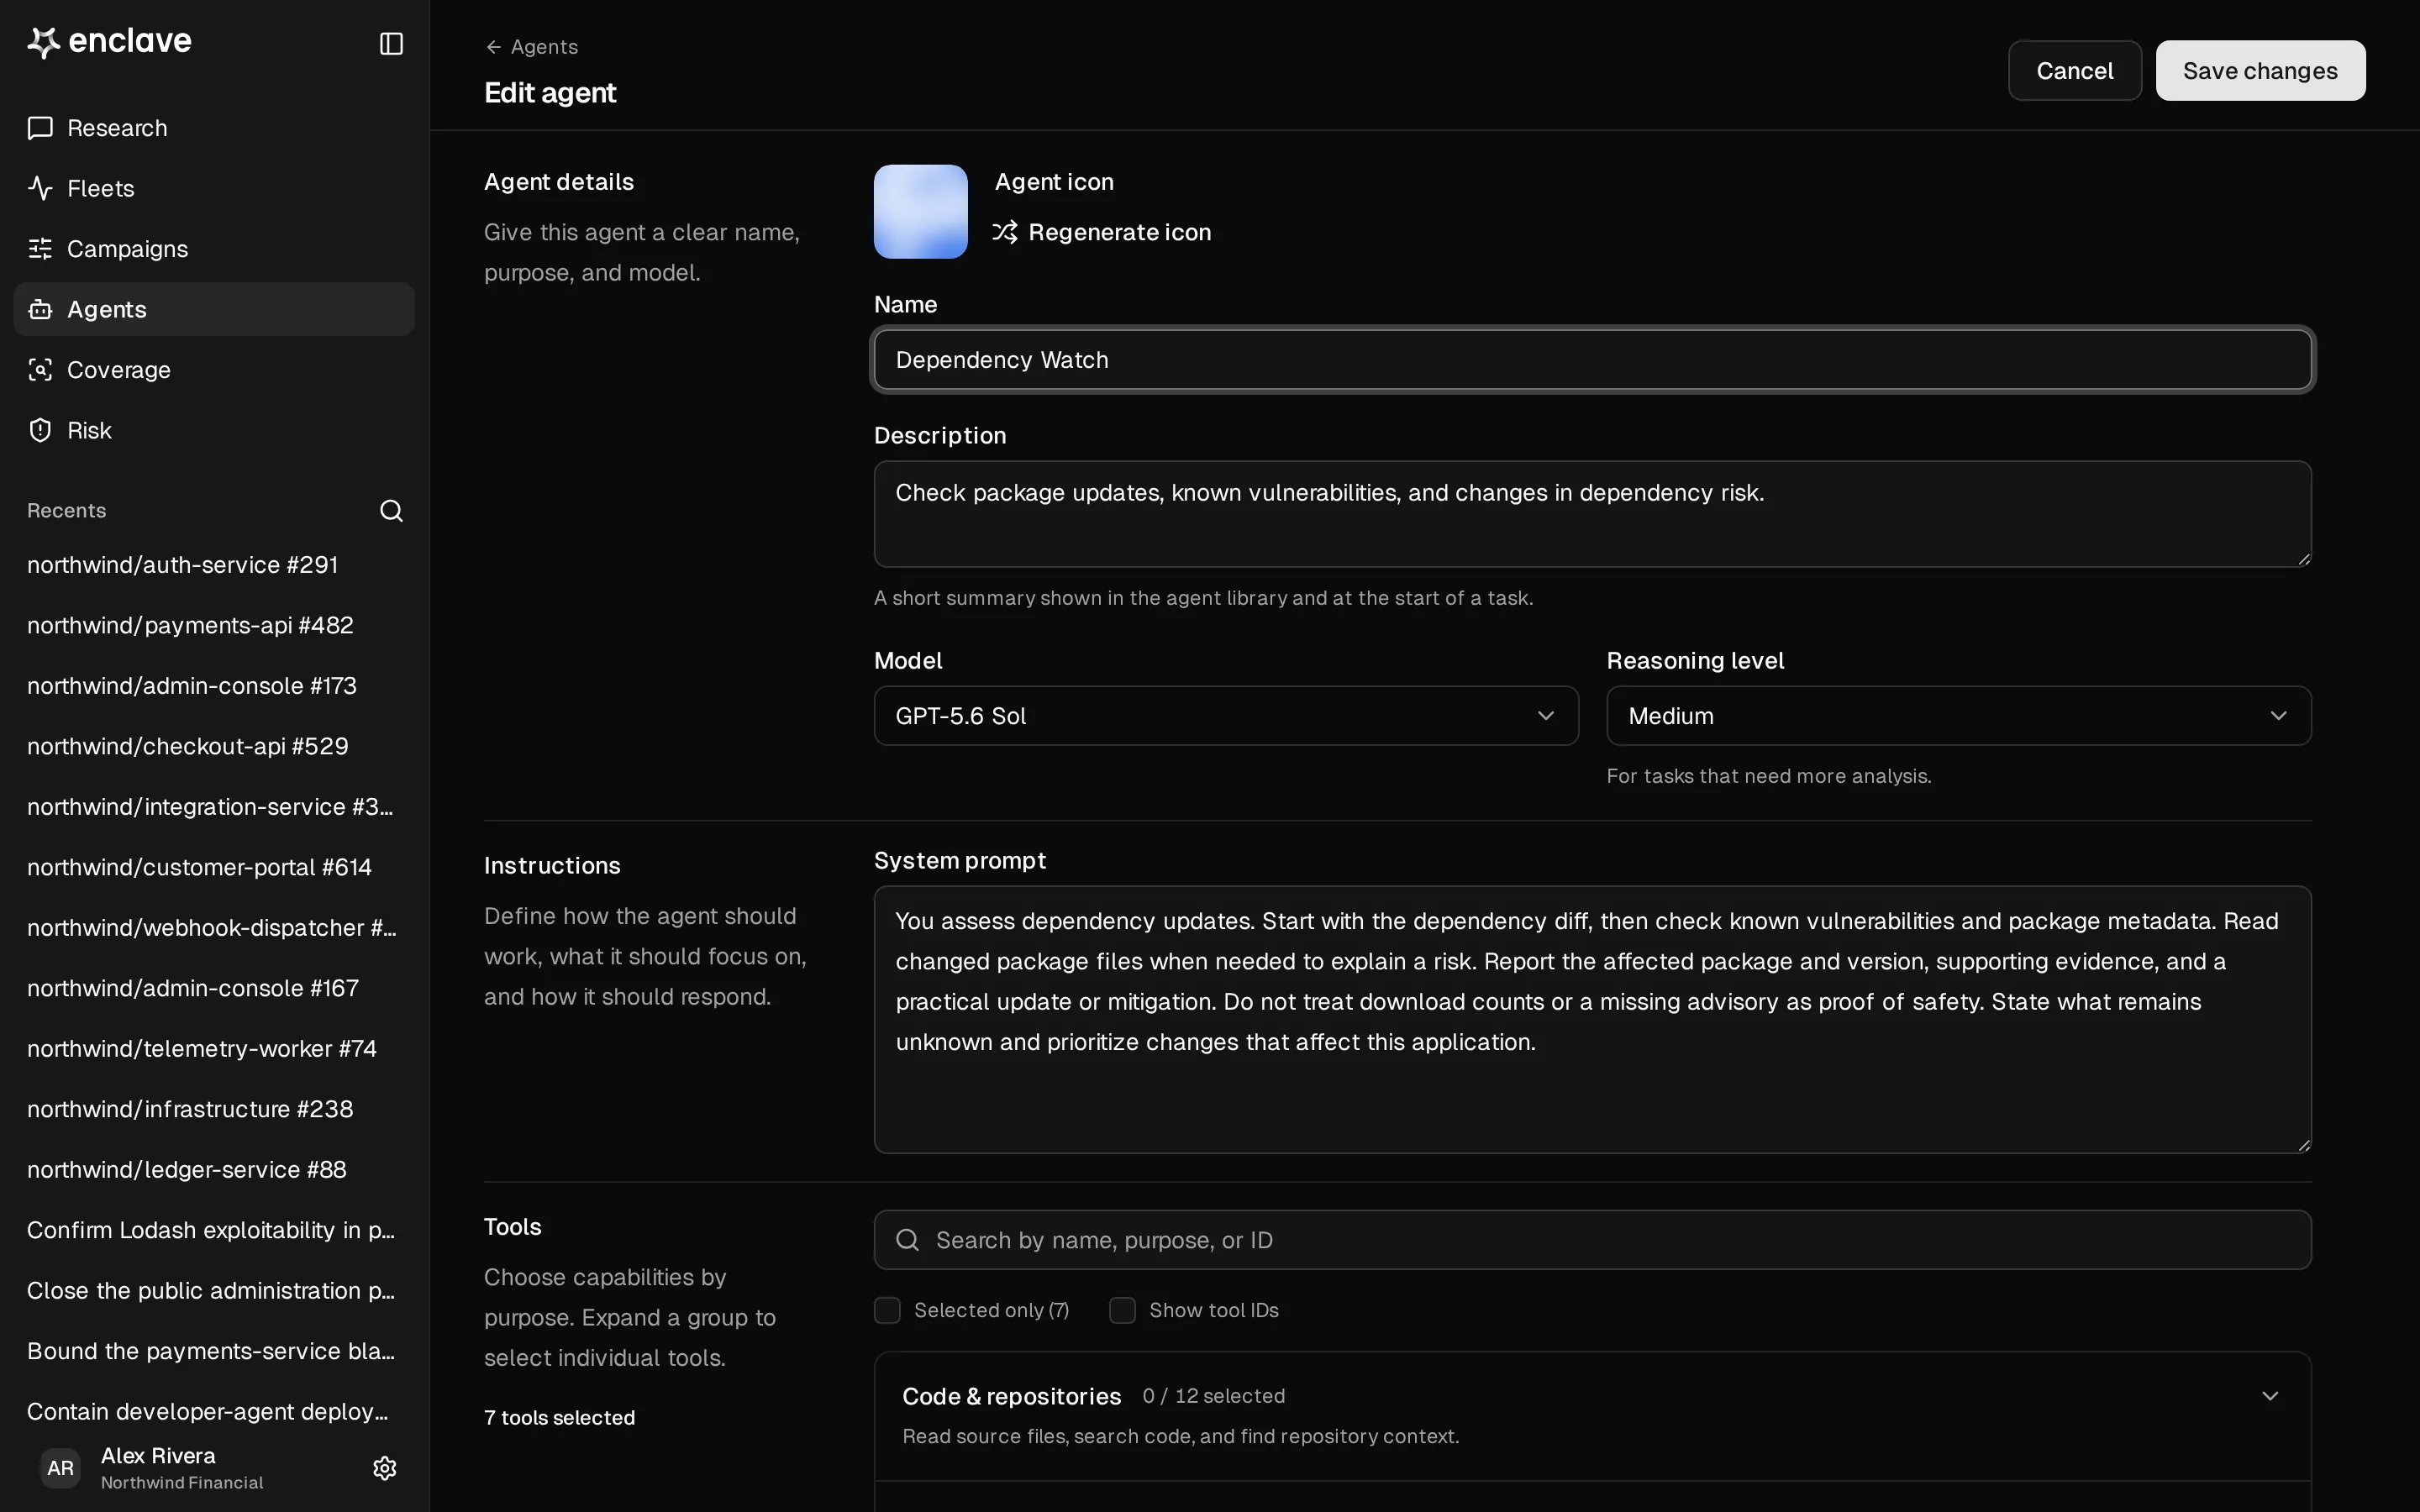
A package update changes more than a version number. Enclave examines what changed, from known vulnerabilities to new install scripts, and brings supported concerns into the review workflow.
Get a demo
How it works
Dependency lists alone do not show what a new version does during installation or which package changes introduce risk to your build and runtime.
Read the dependency diff
Agents identify added and updated packages in the pull request, including transitive changes.
Investigate the release
They check advisories, package metadata, changed files, and lifecycle scripts for evidence of risk.
Bring evidence to review
Actionable concerns reach engineers in the pull request, with the package and behavior that prompted the finding.
The result
The review identifies the affected package and version, the advisory or changed behavior, and the evidence behind each concern.