
Continuous penetration testing
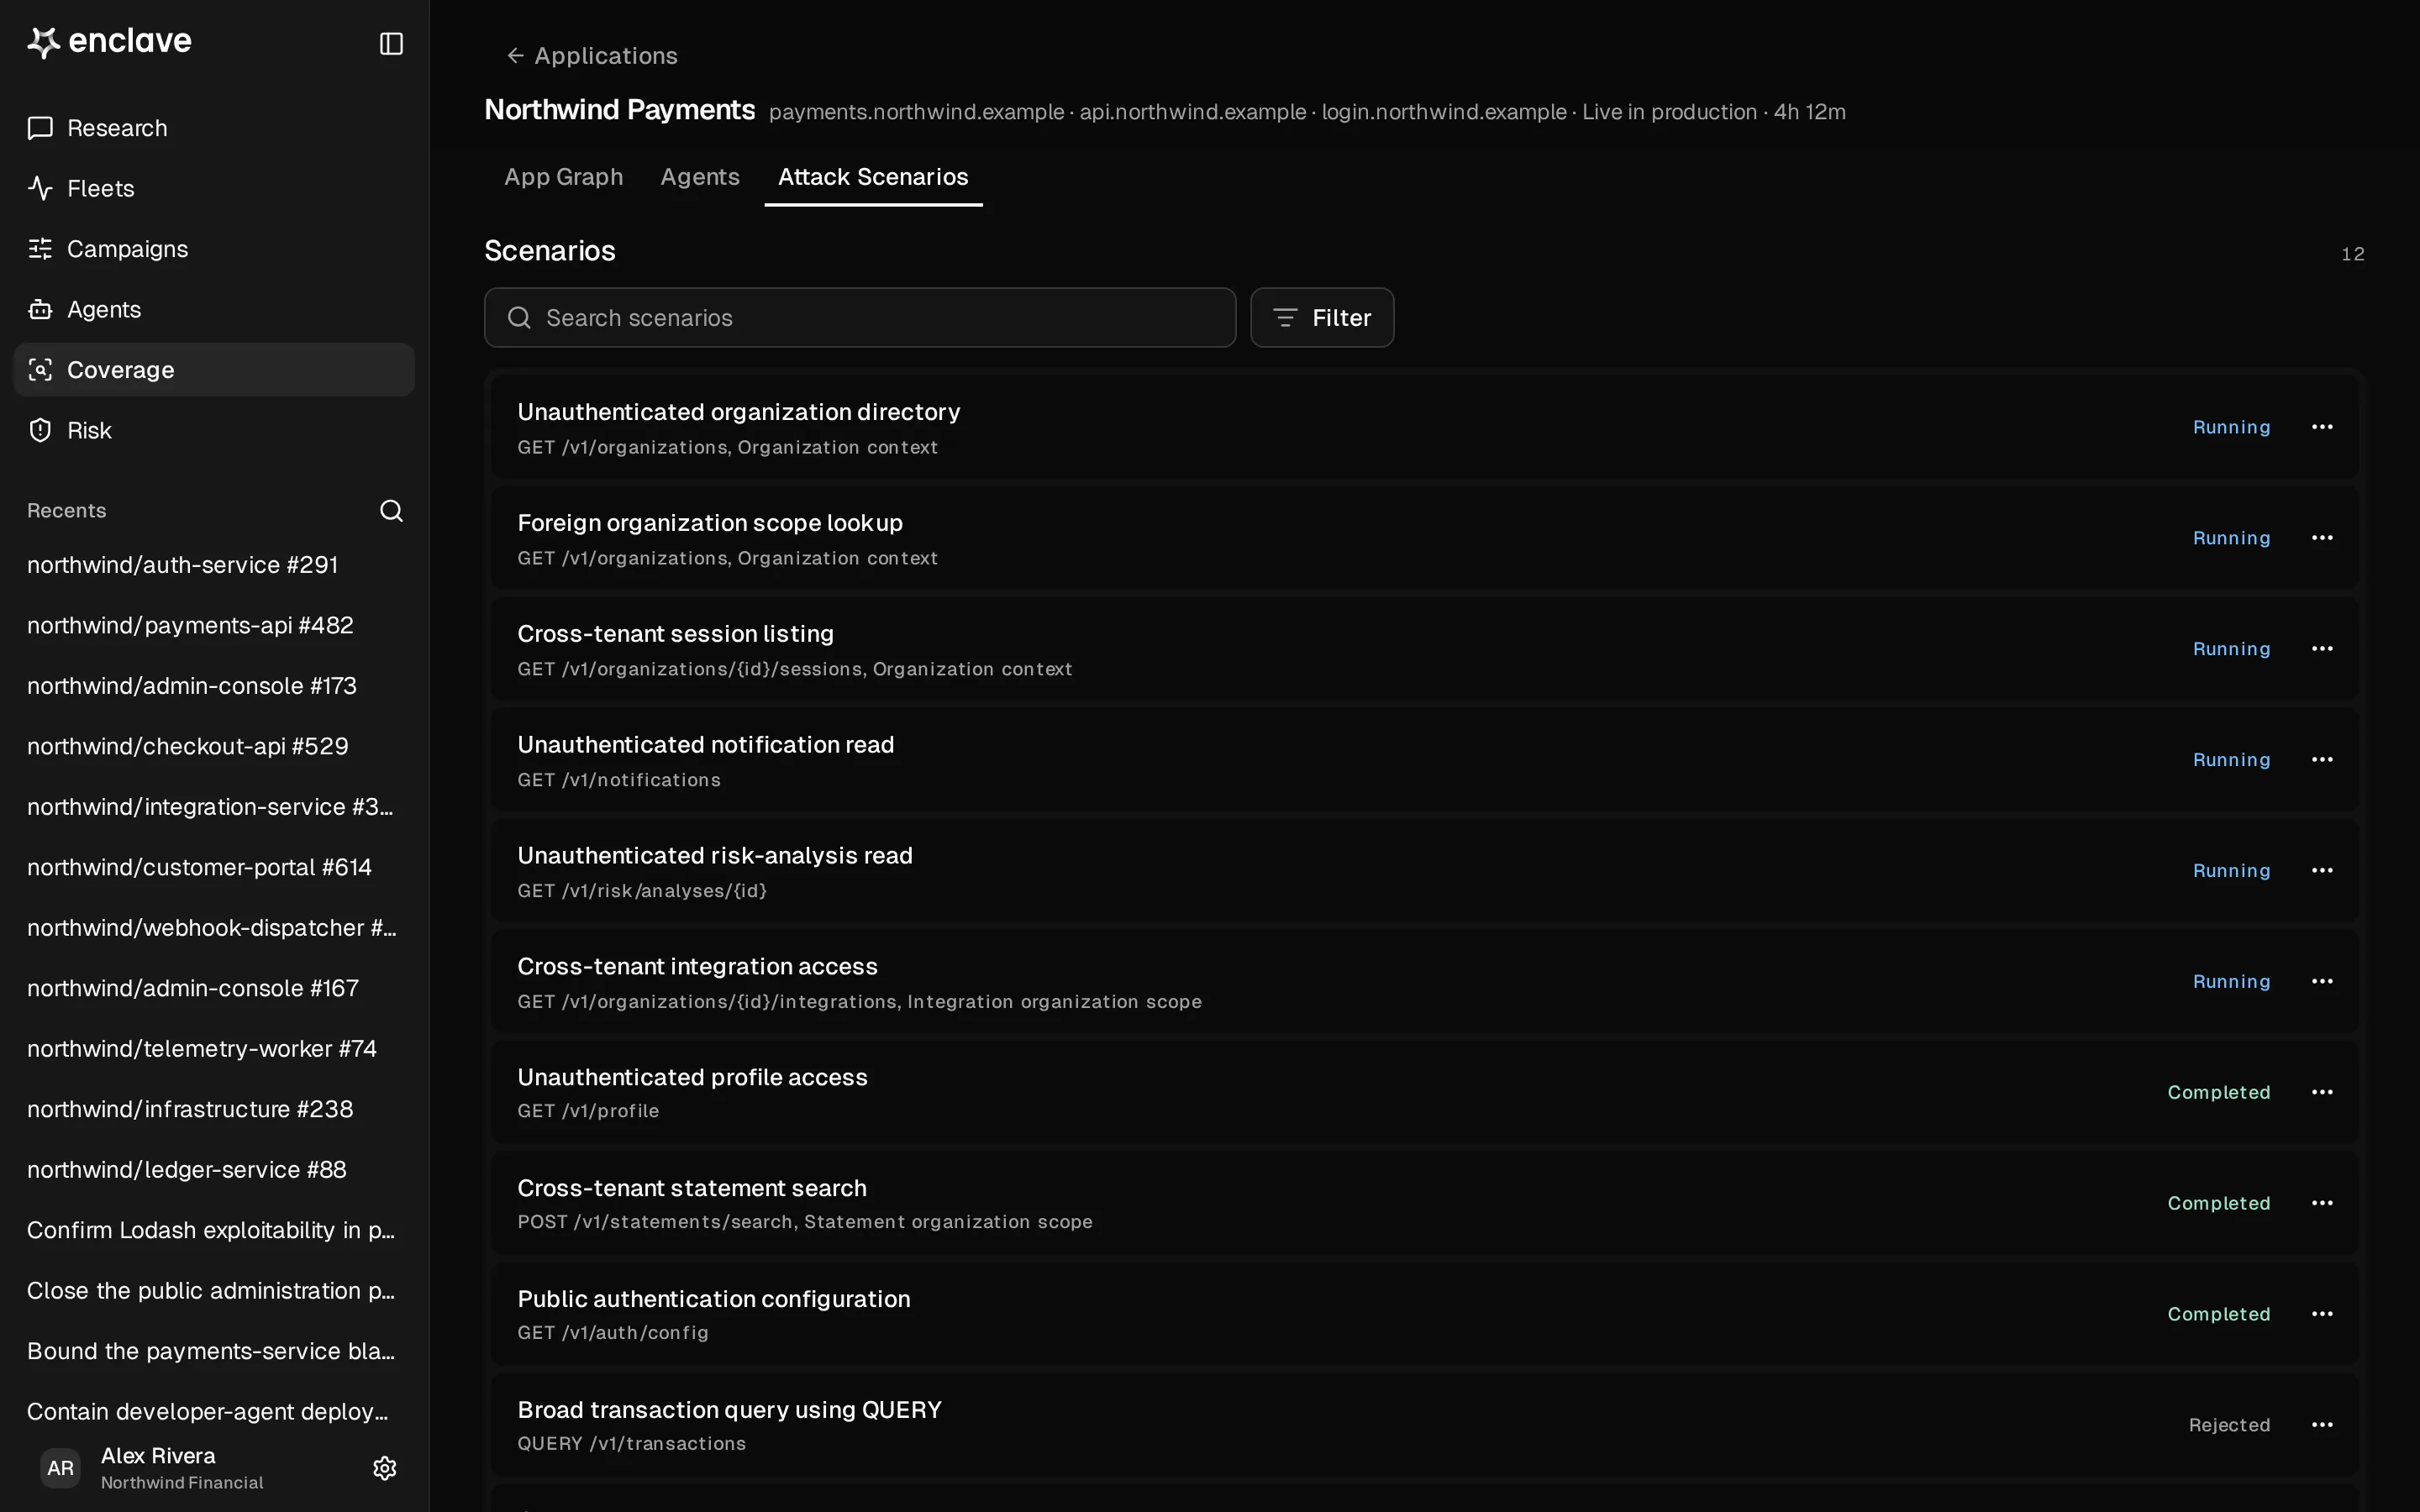
Enclave tests reachable attack paths as code and infrastructure change, records what succeeds, and retests after fixes are deployed.
Get a demo
The workflow
How it works
A point-in-time report tells you what an attacker could do on one day. New services, configuration changes, and code releases change that picture.
Map the environment
Agents inspect reachable assets, services, and trust boundaries to find potential ways in.
Attempt the path
They test suspected weaknesses and collect evidence when an attack actually succeeds.
Retest after remediation
Confirmed attack paths move to triage and remediation. Agents replay the original path after deployment.
The result
Scenario results show what was attempted, which paths succeeded, and whether a deployed fix closed the original route.