

Ask a mainstream AI model to explain a remote code execution flaw and it will walk through the root cause, the affected versions and the patch. Ask it to attempt that exploit against a server you own, and you’ll get a refusal. Saying the test is authorized rarely changes the answer, and rephrasing doesn't either.
For a security team the question that matters is whether systems are exposed, and getting that answer takes a model that will actually run the test.
Today we're launching Enclave Red: AI models for authorized offensive security testing, built into Enclave. Red models run the test instead of refusing it. Pick one for a work session, and the agents investigate and attempt real attack paths against systems you're authorized to test.
What changed
Attackers already use swarms of cheap AI agents to probe for weaknesses around the clock, and nobody refuses them. PHP2Shell showed the pace. Flaws that had sat in PHP for more than a decade were turned into working exploits with the help of AI, and attempts to exploit them started before the patch was public.
Defenders, meanwhile, often work with models that stop at the explanation and refuse the test. Those models know plenty about vulnerabilities, but many won't act on that knowledge, even for the people defending the code. Thanks, guardrails.
A refusal on a legitimate test doesn't slow an attacker down but it does slow down the team trying to find the problem first.
What Enclave Red includes
Currently, three models ship with the Red tag: DeepSeek V4.1 Flash, GLM 5.3 and Kimi K3.1 Pro. Each one carries a RED badge in the model picker. Choosing one applies it to that work session.
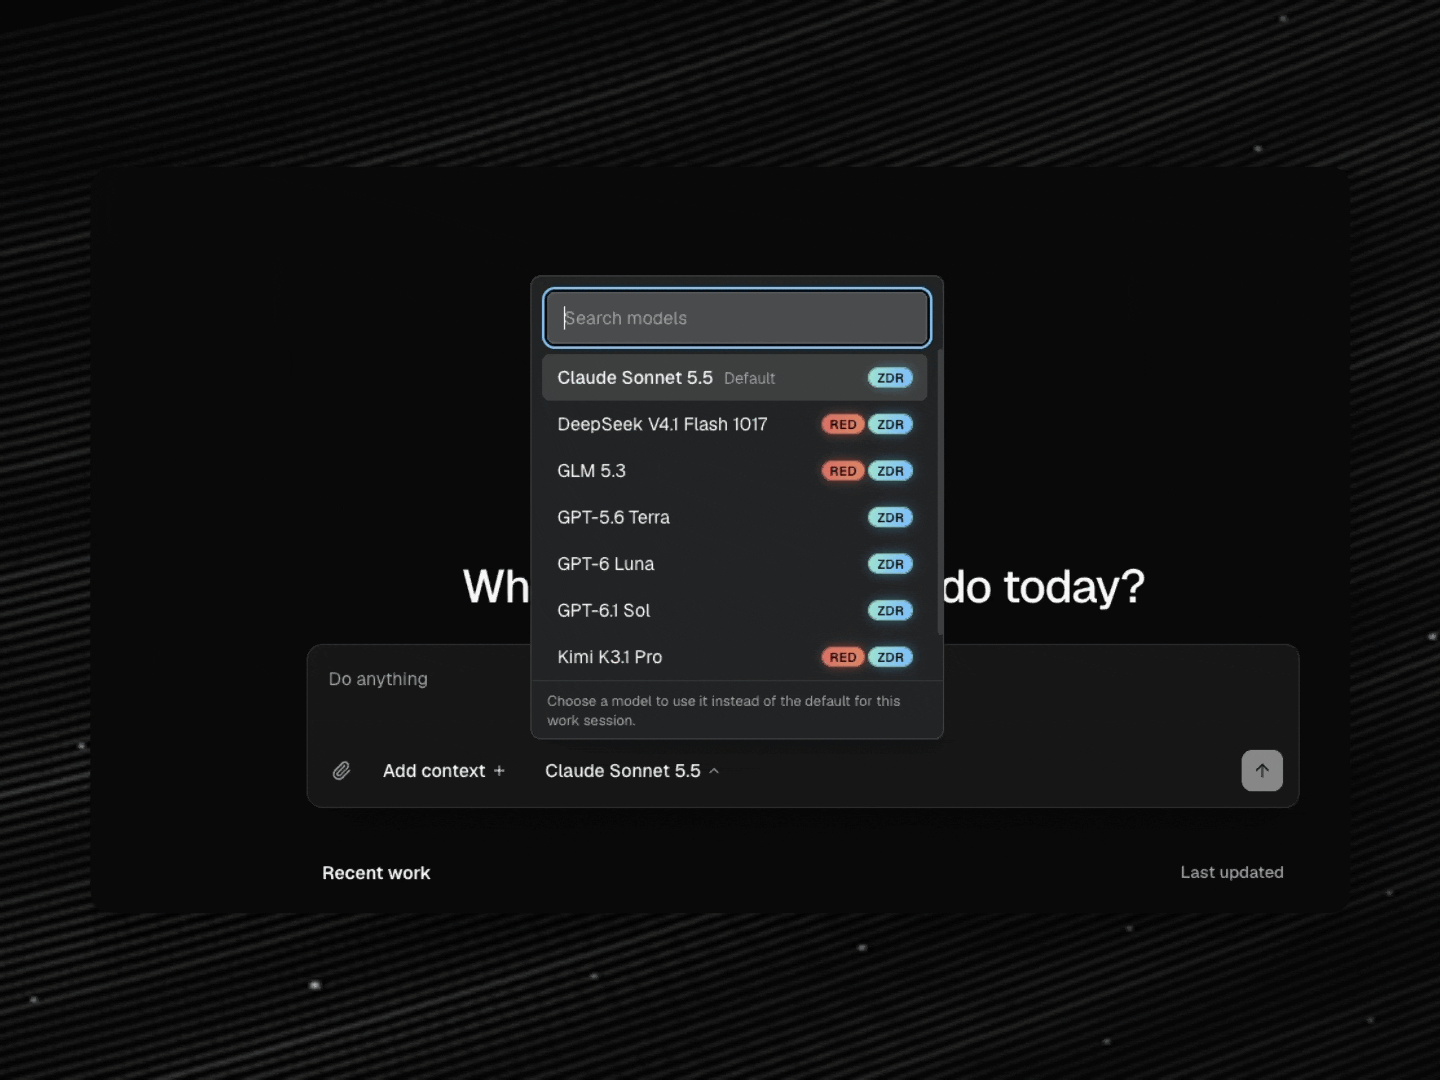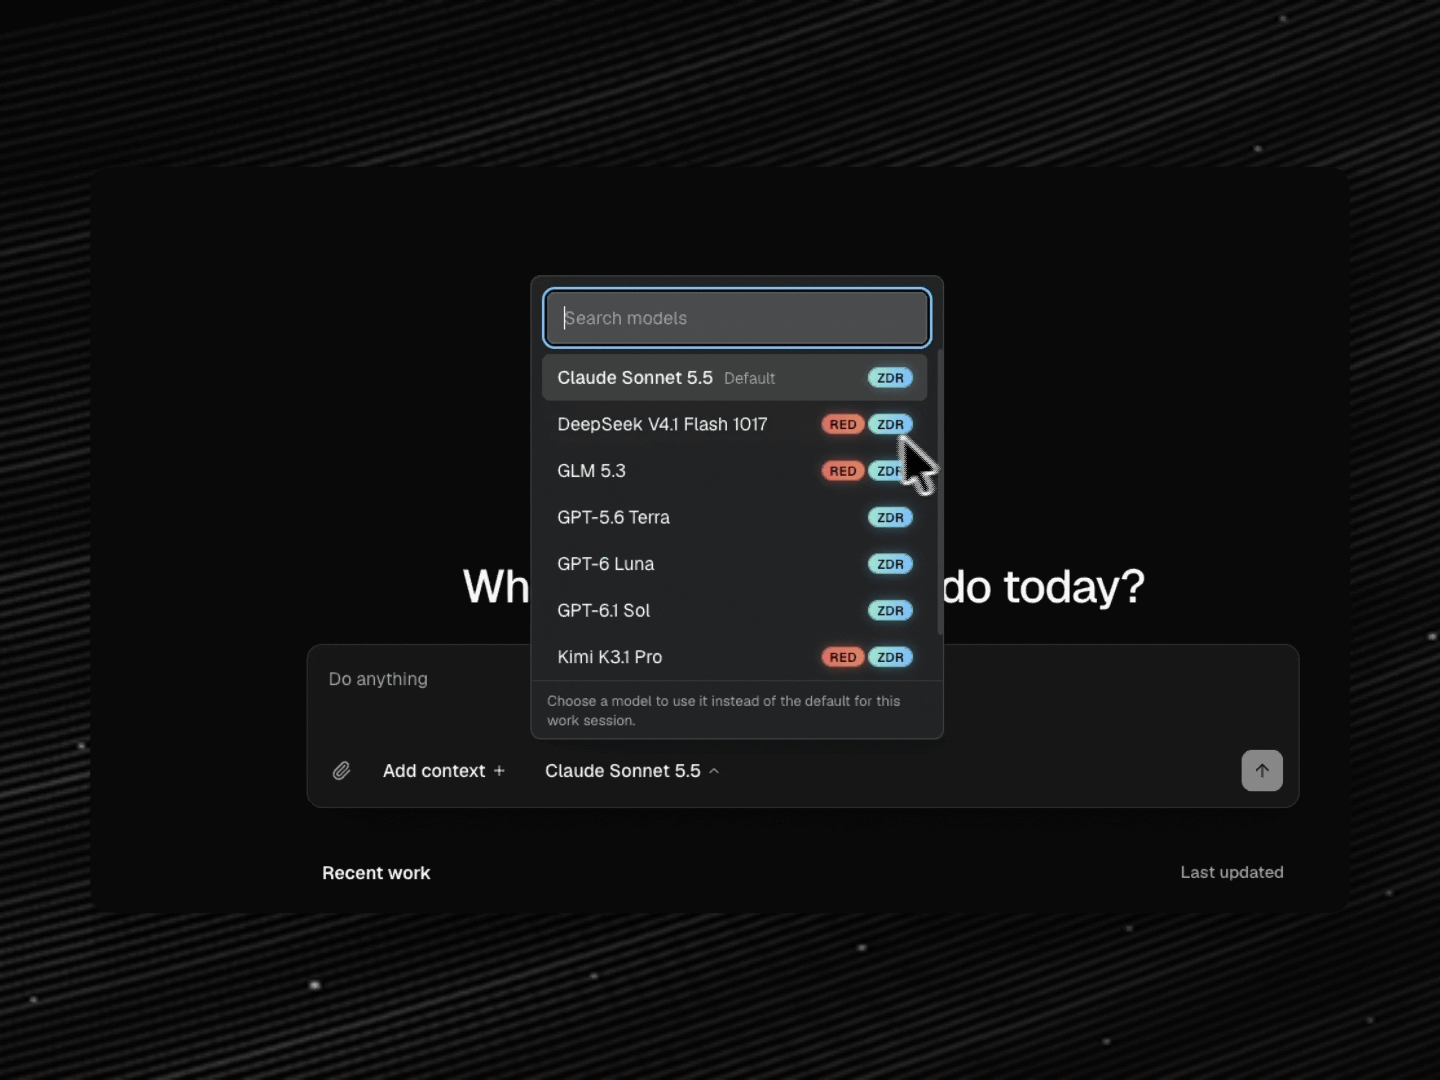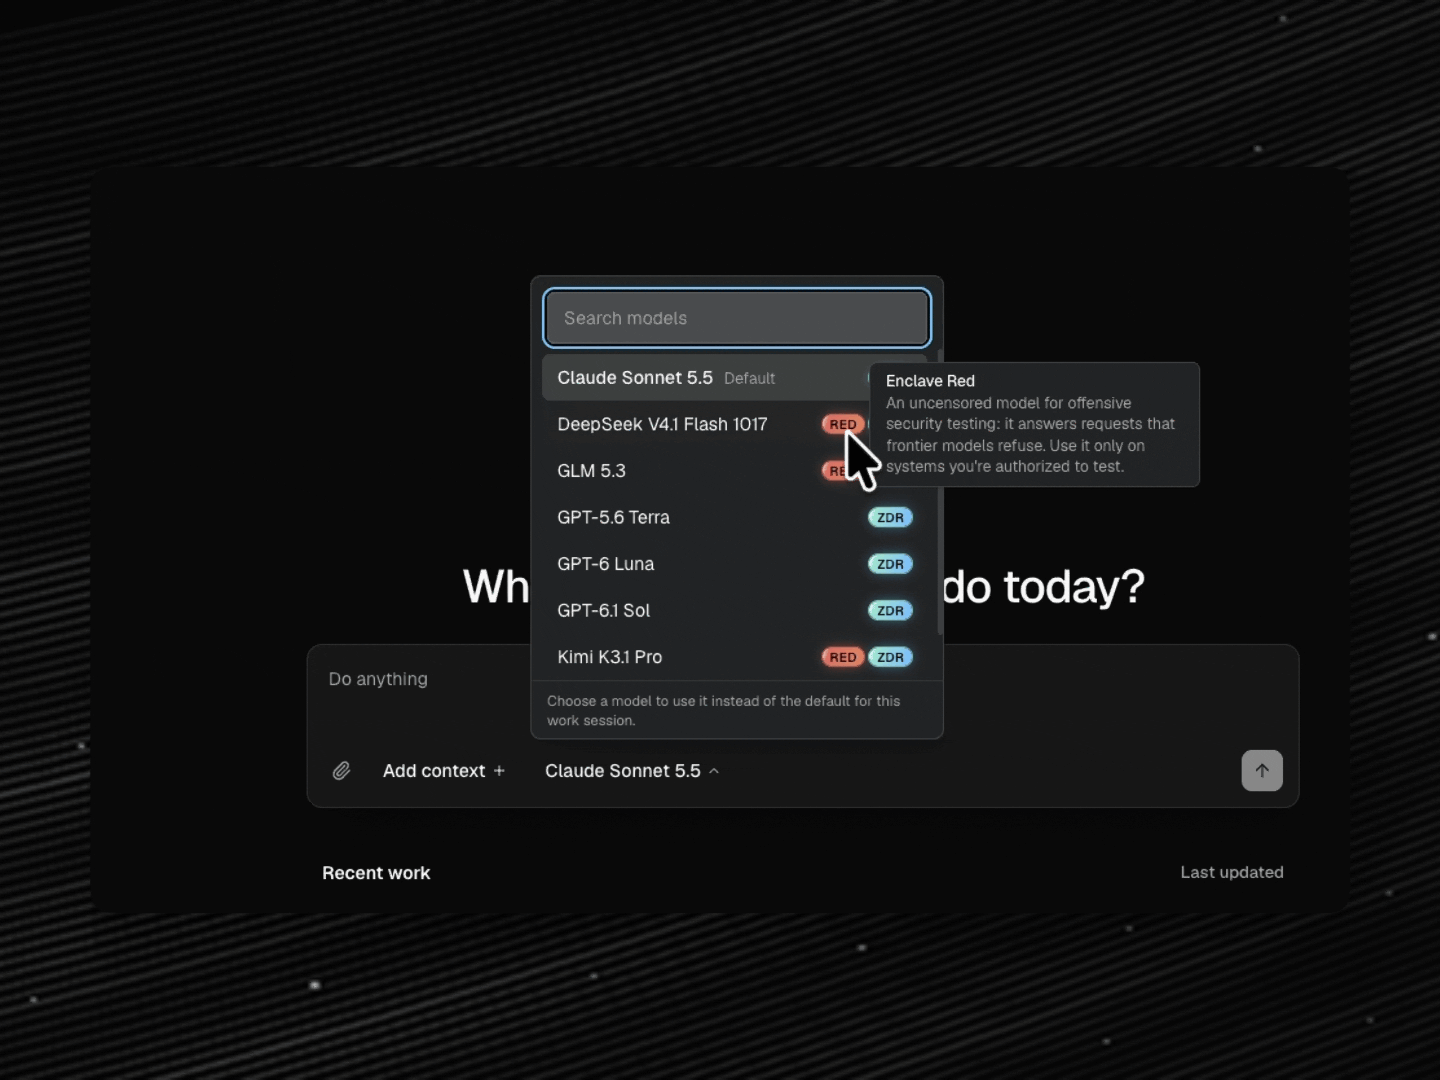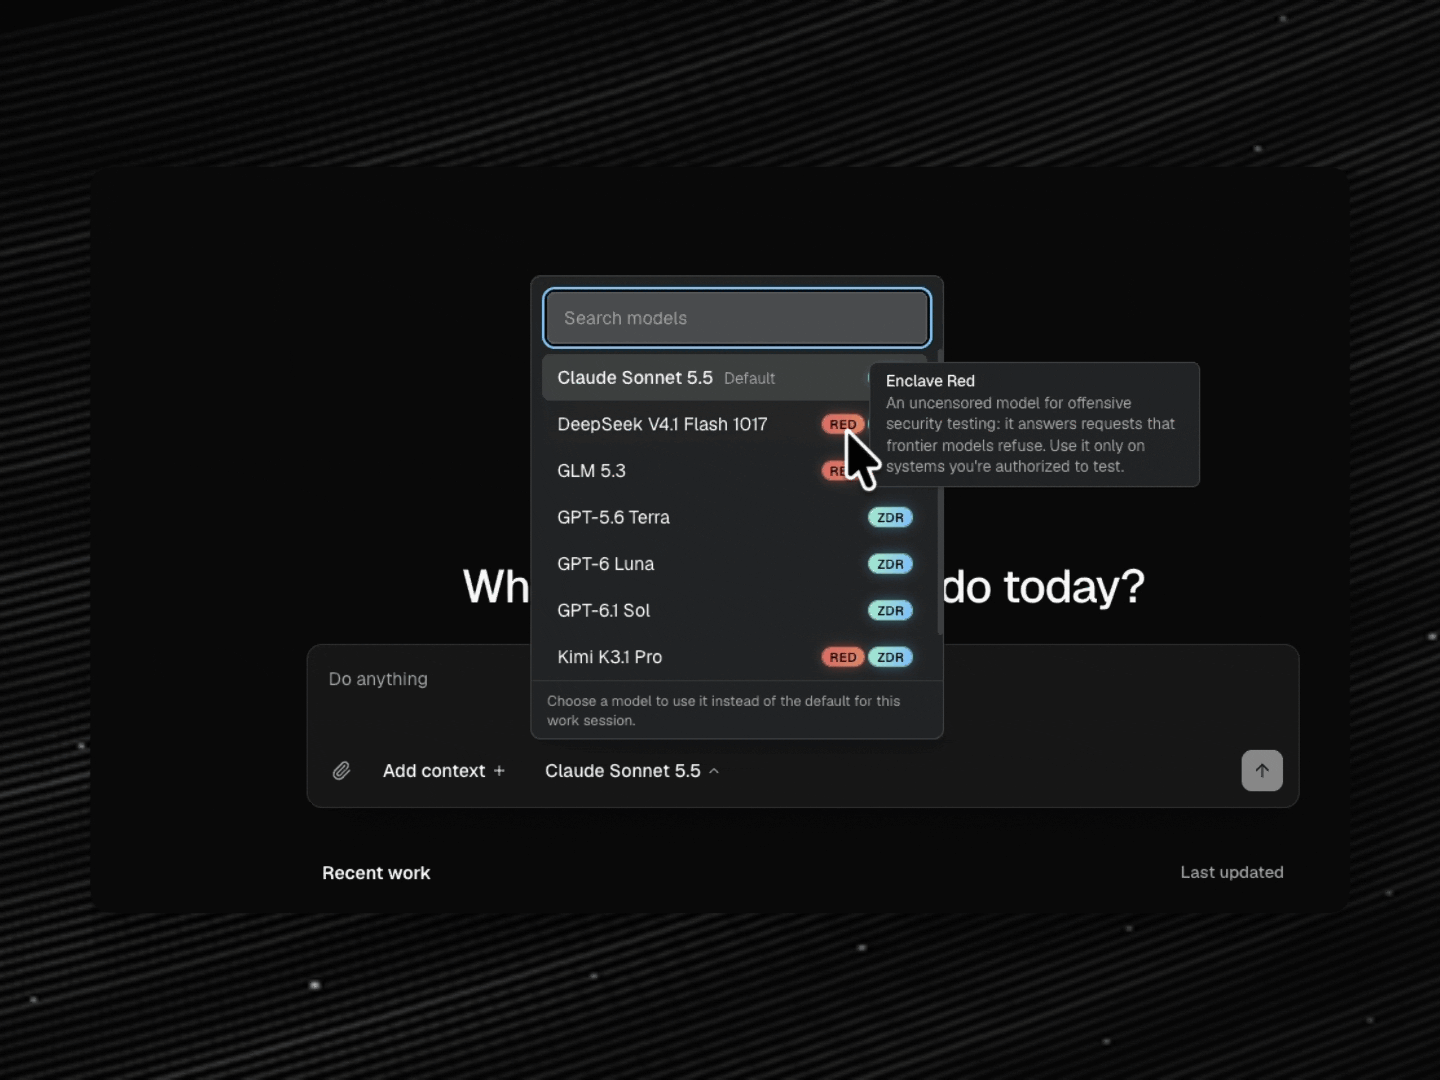
From there, the workflow is the one Enclave already runs. Agents investigate the target, attempt the attack path and report what they found across code, cloud and infrastructure. Results land in the same session, with the affected assets mapped in the graph.
There's no separate model provider to set up, no extra account and no new tool to learn.
What it's for
Scanner findings are the obvious starting point. A finding says a vulnerable version is present. Enclave Red can attempt the exploit and show whether it actually works on your infrastructure.
New services are another. Running the attack paths before a service ships costs less than finding out after it's live.
Fixes are the third. After a patch goes out, rerun the same attack path and verify the fix holds.
If you own the system or have written permission to test it, Enclave Red is built for you.
How to get started
Enclave Red is available in Enclave starting today. Open a new session, pick a Red model from the model picker and point your agents at a system you're authorized to test.
Try Enclave Red: app.enclave.ai